Resources
    Product Updates
    Issue 04 · May 2026

    What's New in Atakama

    A roundup of the latest features, enhancements, and console improvements shipping across the Atakama managed browser this release.

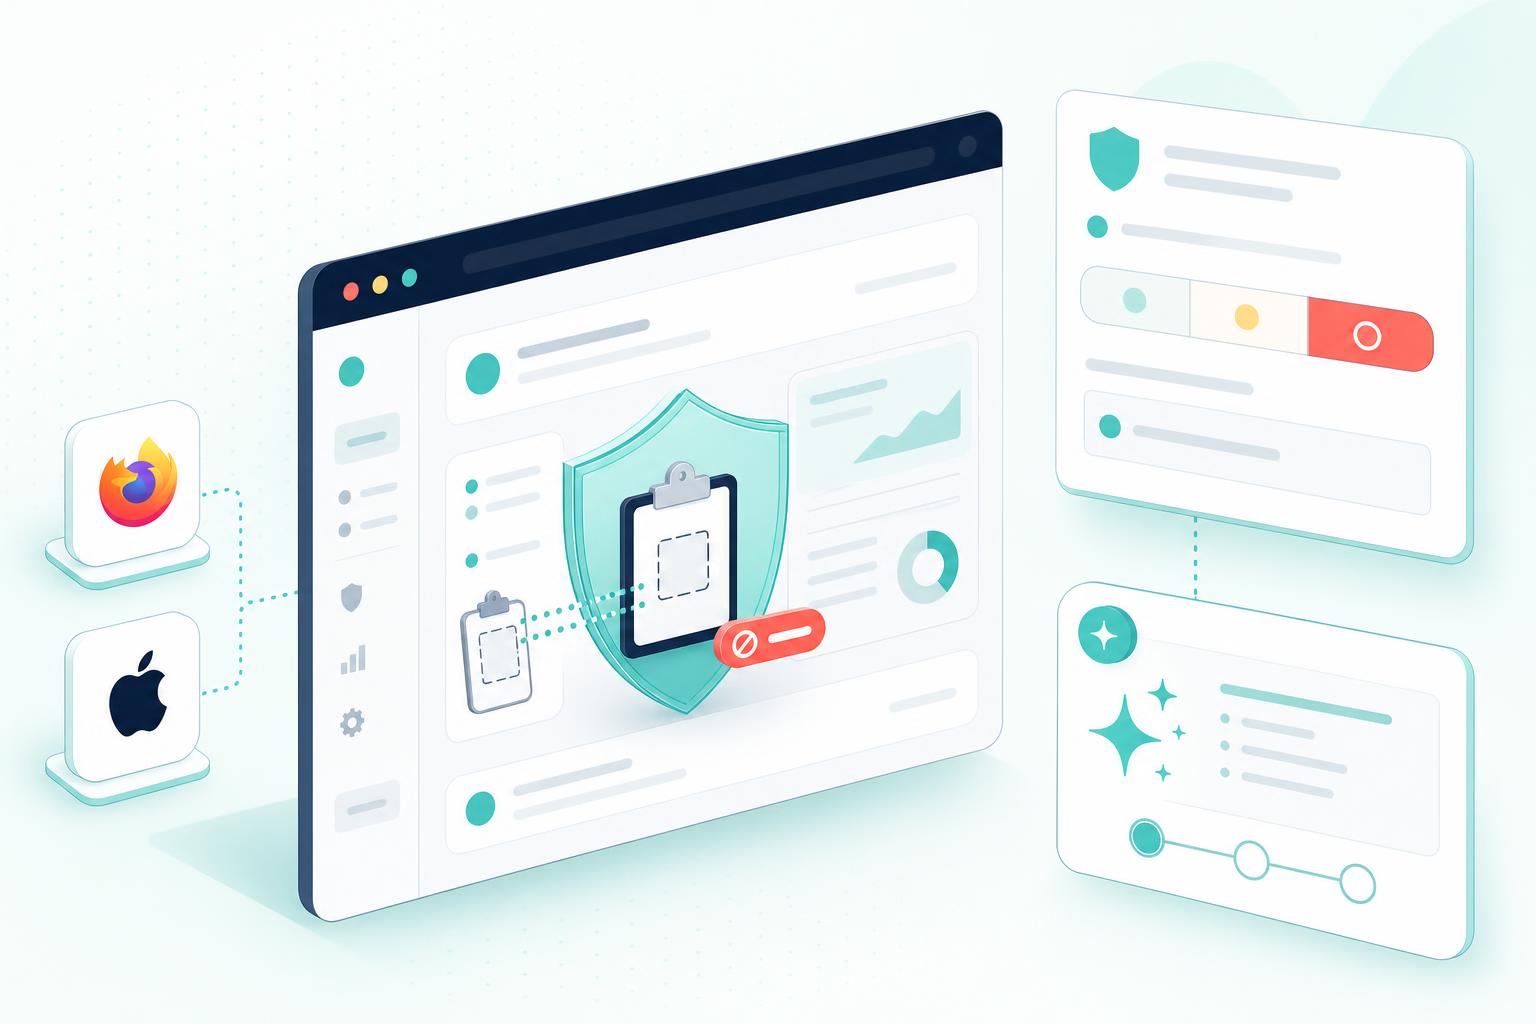
    Illustration of Atakama product surfaces: browser shield, policy toggles, AI sparkle, credentials key, and extension puzzle piece

    New Features

    Block Pastes to Websites

    Create policy rules that prevent users from pasting content into specific websites. An added layer of browser-based data protection that reduces the risk of sensitive information ending up in unsanctioned or risky web applications.

    AI Controls Wizard

    A guided flow for building AI usage policies, making it faster to roll out Allow, Warn, and Block rules across sanctioned and shadow AI apps without piecing together individual settings.

    Firefox Extension Auto-Install (Windows)

    Atakama now automatically deploys and manages the Firefox extension on Windows endpoints, bringing it in line with Chrome and Edge for consistent browser coverage.

    macOS Installer in the Tools Page

    A new Mac tab on the Agent & Extension page provides download buttons for the RMM install script, uninstall script, and .pkg file, plus links to the Mac feature support guide and extension login prompt configuration.

    Redesigned Security & Compliance Page

    A full event table with filterable, sortable columns, colored action badges, and CSV export, making it easier to review and report on activity.

    Console UI Improvements

    The Management Console has a refreshed visual theme, with updated colors, buttons, fonts, and component styling for a cleaner, more consistent experience across all pages.

    Enhancements

    Smarter Safe Mode

    When a trusted website contains embedded malicious resources (such as a flagged icon or script), Atakama now loads the page while silently blocking only the malicious sub-resources. Previously, the entire page would be blocked. This reduces unnecessary disruption for users while maintaining full protection against malicious content.

    Credentials Warning Logs

    We've added credentials warning logs to the Credentials Analysis page, giving administrators improved visibility into risky credential events.

    Clearer Rule Action Controls

    Allow, Block, and Warn actions now appear as clearer multi-choice selectors with distinct visual states, and toggle switches have replaced the old enabled/disabled buttons, for a more intuitive policy configuration experience.

    Bug Fixes

    We've also resolved a number of issues, many focused on DNS reliability and internal resource access.

    Internal domains intermittently not resolving

    Closed a brief DNS gap during dock/undock events on Windows laptops with docking stations.

    Split-DNS not routing .local queries to domain controllers

    Internal queries now reach local domain controllers, restoring mapped drives and internal resources.

    NRPT rule not auto-created when DNS is re-enabled

    The rule is now reliably created when DNS is re-enabled via policy.

    DNS proxy timeouts causing degraded resolution

    Fixed timeouts under heavy query volume that were adding latency.

    Local domain access lost after network changes

    Resolved a third-party software conflict that dropped local domain access until restart.

    Entra-joined users not appearing in the admin console

    Active Entra-joined users who sign into Office 365 now appear correctly.

    Extension icon showing "Not Logged In" for authenticated users

    Logged-in users no longer see a false red warning on the extension icon.

    Password strength not captured for Okta logins

    Password grades are now recorded for Okta login events.

    See These Updates in Action

    Walk through the new console, paste-block policies, and AI Controls Wizard with our team.

    Newsletter

    Stay ahead of browser threats

    Get monthly security insights, product updates, and expert guides delivered to your inbox.

    No spam. Unsubscribe anytime.